
← All use cases
Use case · Control
One audit trail for all AI — in your SOC
Regulators, auditors and customers increasingly ask how you use AI. WALLIOO records every policy decision across browsers, agents and apps in one consistent format — and streams it to the tools your security team already uses.
Who it is for
DPOs, CISOs, auditors and SOC teams that must answer who used AI, and with what data.
What it covers
Every decision from Browser Guard and Gateway — employees, agents and apps — in one event format.
What you get
- Answer an audit in minutes
- AI events in your SOC, by syslog or SIEM
- Ready-made dashboards for CISO, DPO and IT
The problem
What goes wrong without control
- Evidence is spread across AI vendor consoles, each with its own format.
- Logs that contain full prompts become a new sensitive-data store.
- Investigations take days of manual work.
How WALLIOO solves it
The flow
Browser GuardChrome · Edge
GatewayMCP · API

Control
Collect
Normalize
Search
Export
Every decision recorded in WALLIOO Control
SplunkSIEM
Microsoft SentinelSIEM
ReportsDPO · CISO
In the product
What your teams see
Real WALLIOO screens, with example data.
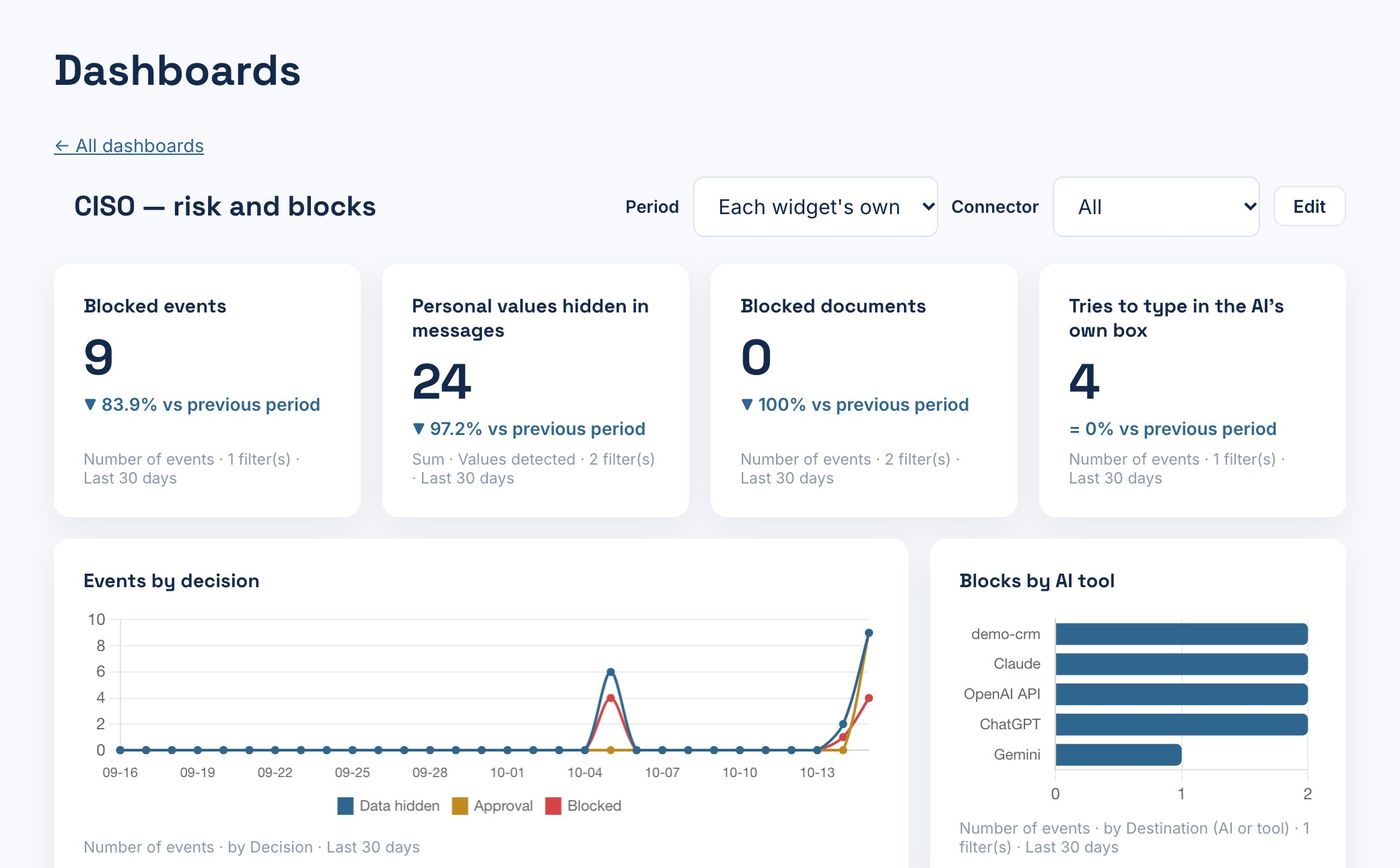
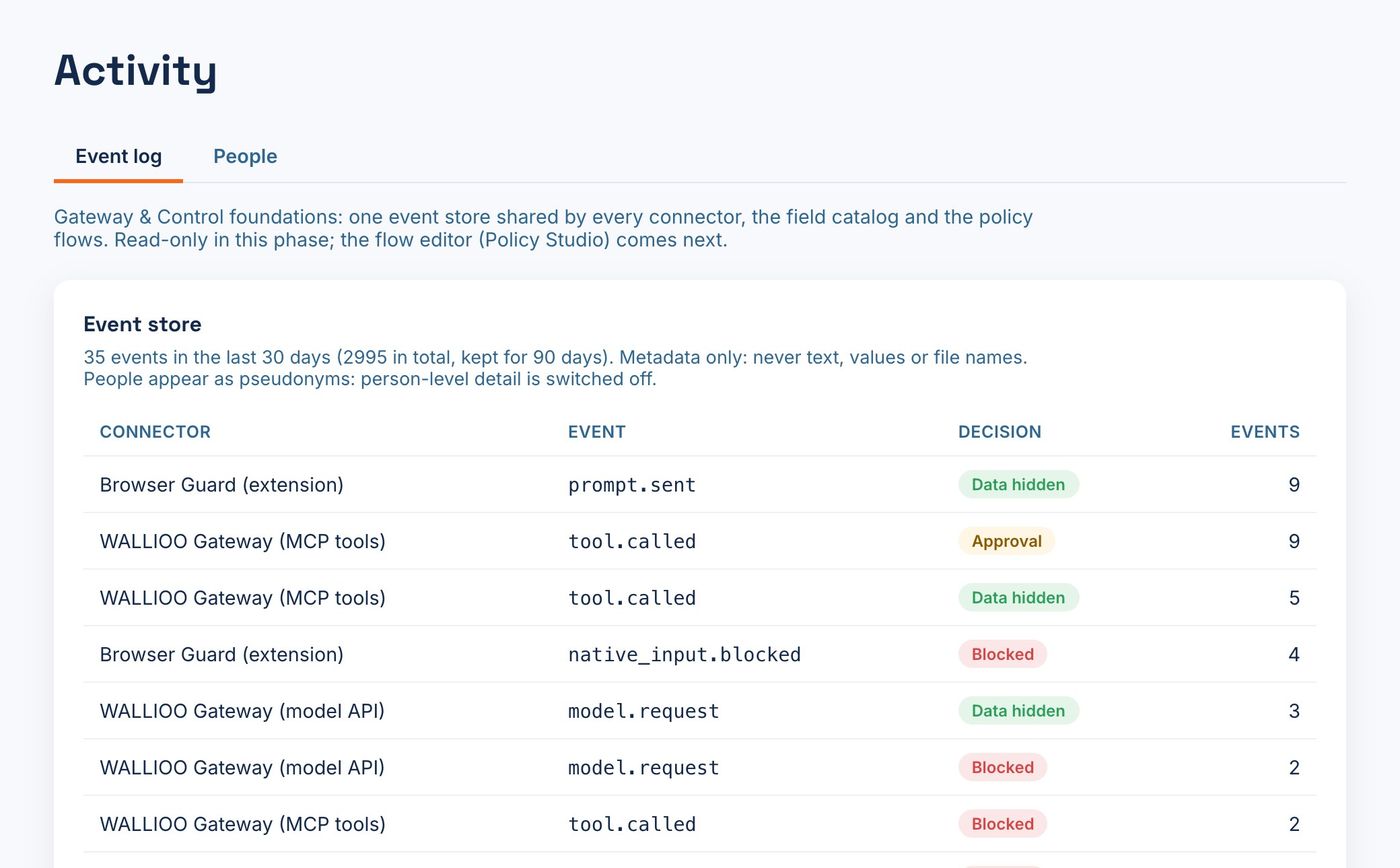
What each event contains
| Field | Answers | What happens |
|---|---|---|
| Actor | WHO | Employee, agent or application — linked to your identity provider. |
| Channel and destination | WHERE | Browser Guard → ChatGPT, Gateway → ServiceNow… |
| Policy and decision | WHAT | Which rule matched and what WALLIOO did: allow, mask, block, approve. |
| Time and context | WHEN | Timestamp, data categories and approver — never the content. |
Works with
SyslogSplunkMicrosoft SentinelElasticMicrosoft Entra IDOkta
The outcome
Answers in minutes
Search by person, AI, tool, policy or decision.
Evidence, not exposure
Metadata only: the audit trail holds no prompts.
Fits your stack
Events flow to your SOC by syslog, or into the SIEM you already run.