
Using AI safely at work.
Practical guides on generative AI, personal data, AI agents and regulation — for IT, security and compliance teams.
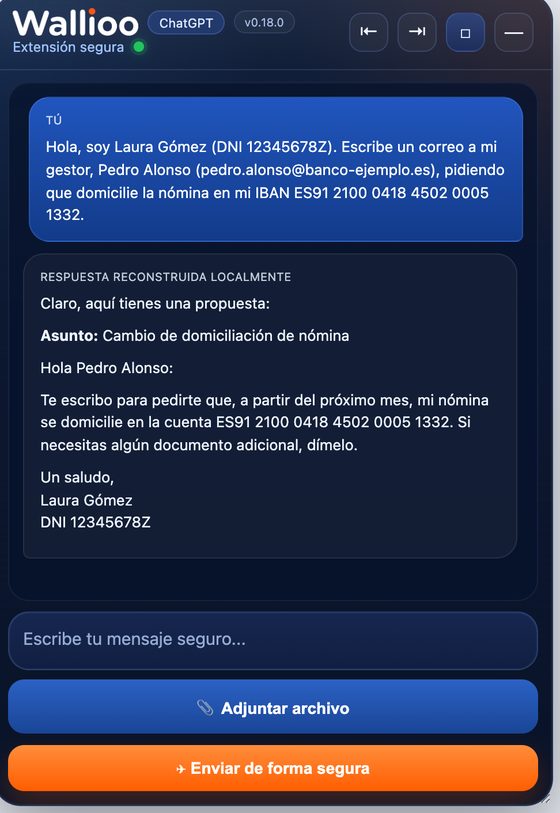
How to use ChatGPT at work without breaking GDPR
Employees paste customer data into ChatGPT, Copilot and Claude every day. What GDPR expects, why policies alone fail, and how to keep the productivity without the data leaks.
Read the article →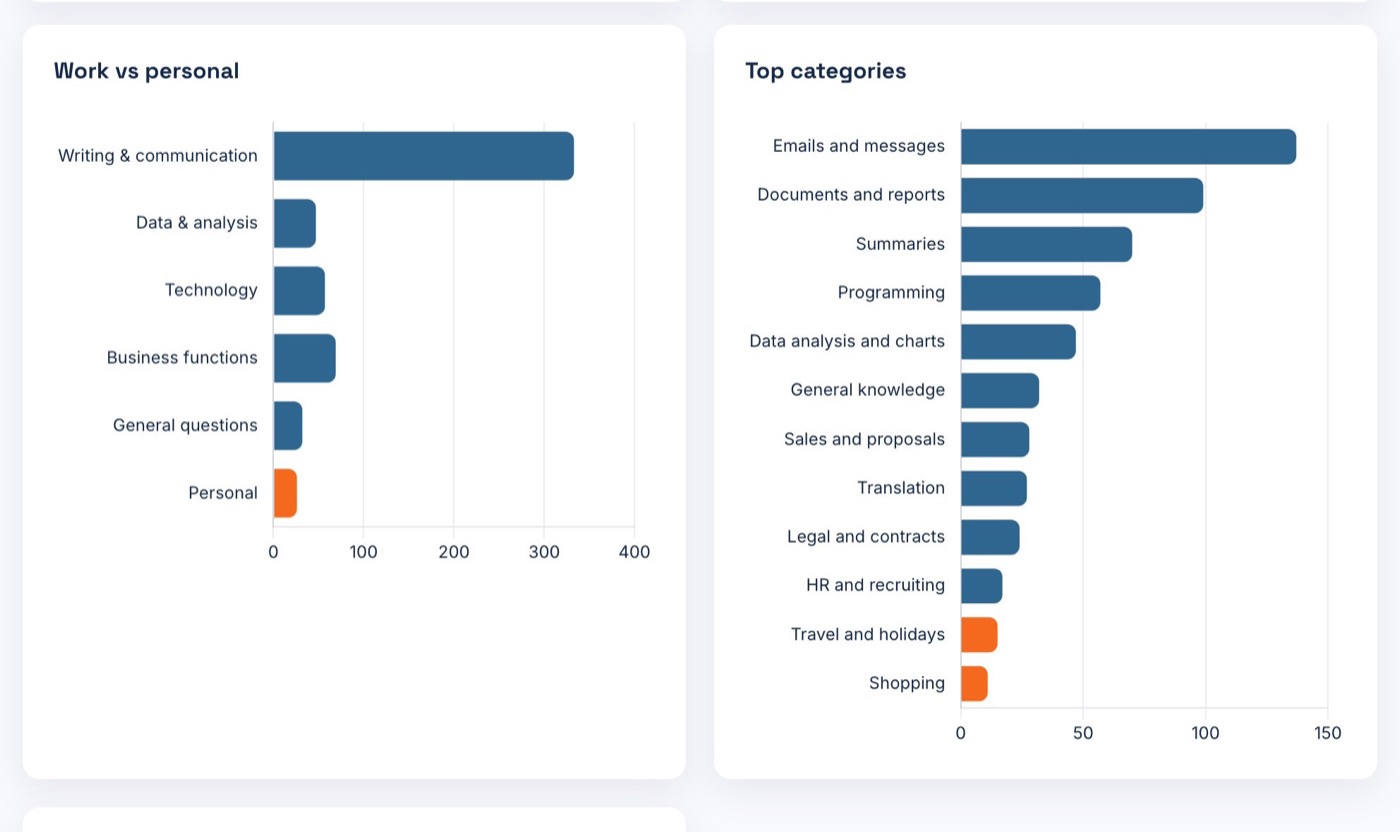
Shadow AI: why banning ChatGPT doesn’t work — and what does
Employees use AI tools IT never approved. Why blocking them backfires, and how to turn shadow AI into visible, governed AI without slowing anyone down.
Read the article →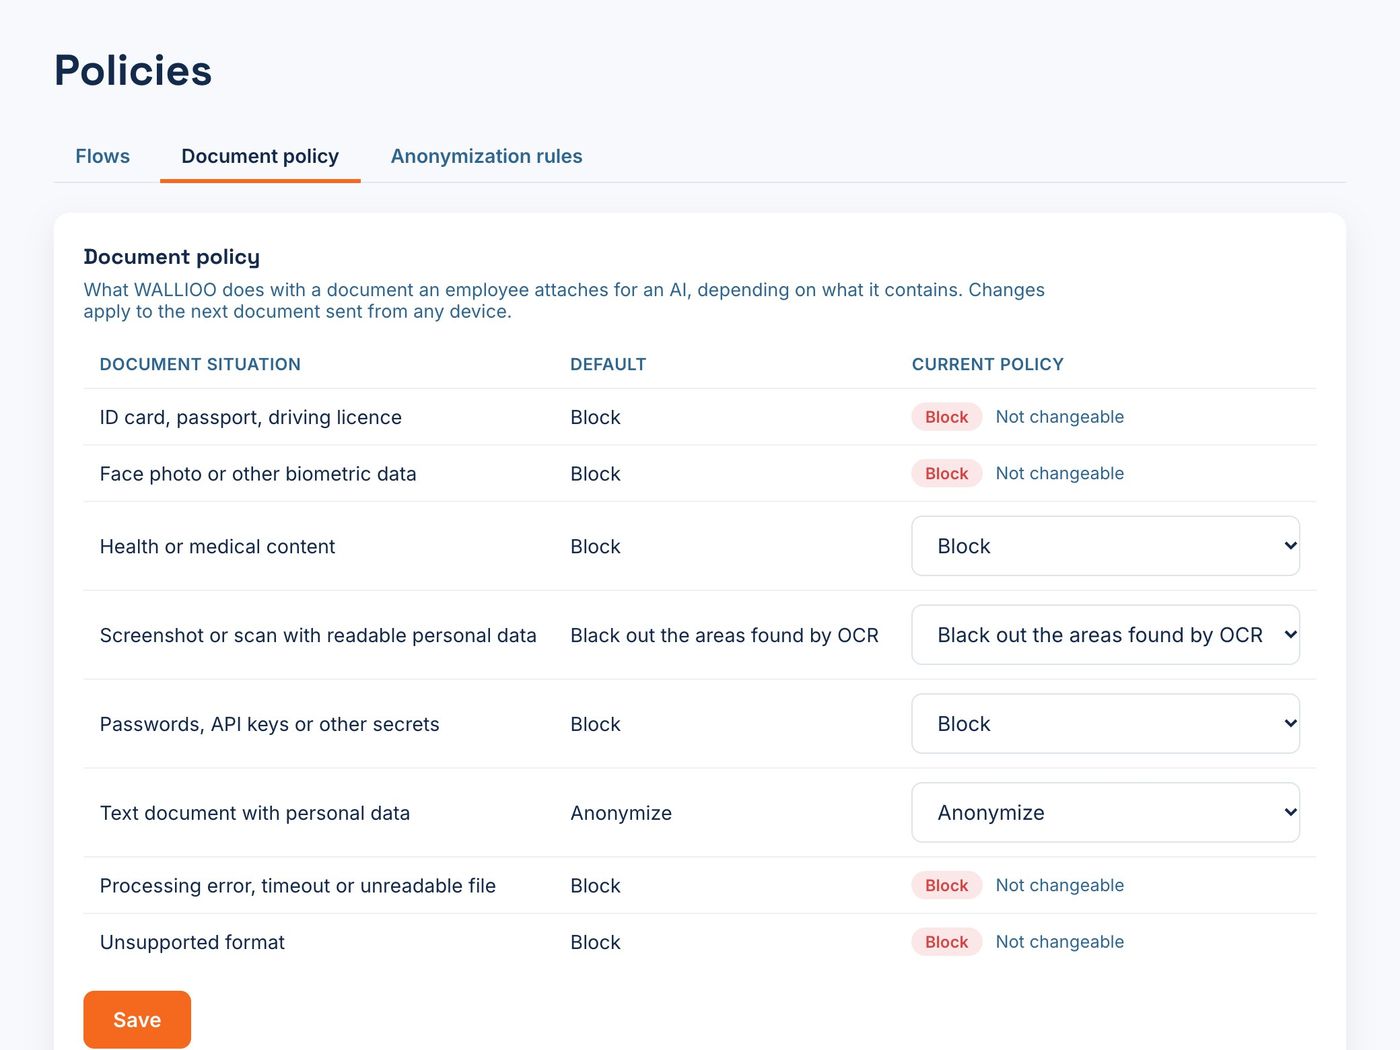
How to anonymize documents before sending them to ChatGPT or Claude
Contracts, payslips and customer lists are full of personal data. Manual redaction, why it fails, and how to anonymize files automatically — and get the AI’s output back with the real values.
Read the article →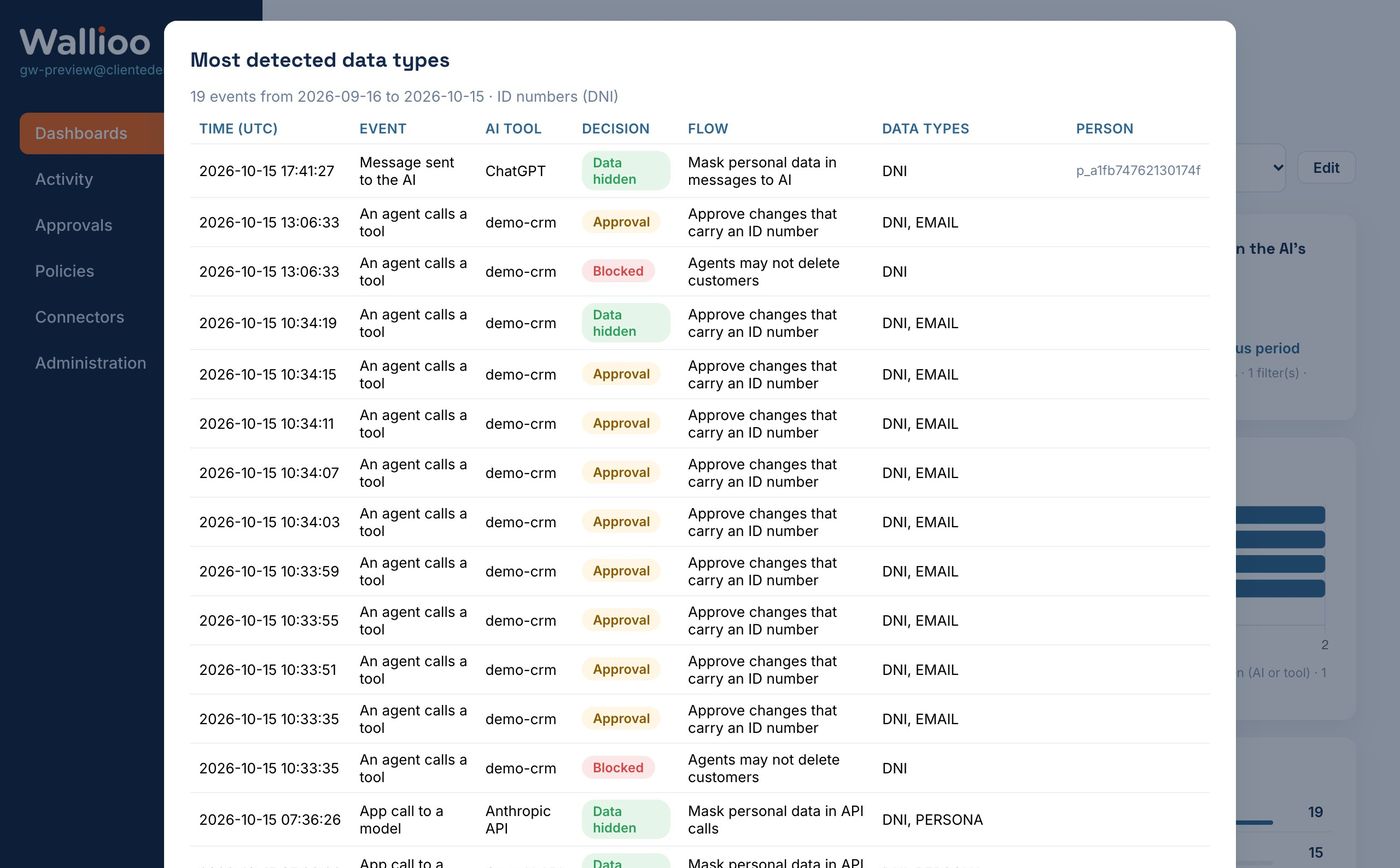
Securing AI agents and MCP tools: least privilege, approvals and audit
AI agents now read and change data in ServiceNow, CRMs and internal APIs through MCP. The risks — inherited privileges, sensitive data, no audit trail — and the controls that address them.
Read the article →
The EU AI Act for companies that use generative AI: what applies today
Most companies are “deployers” under the EU AI Act, not providers. The obligations that already apply — like AI literacy — and the practical evidence you will be asked for.
Read the article →